FomoPeek iOS Malware: Unpacking a Sophisticated Kernel-Level Crypto Theft
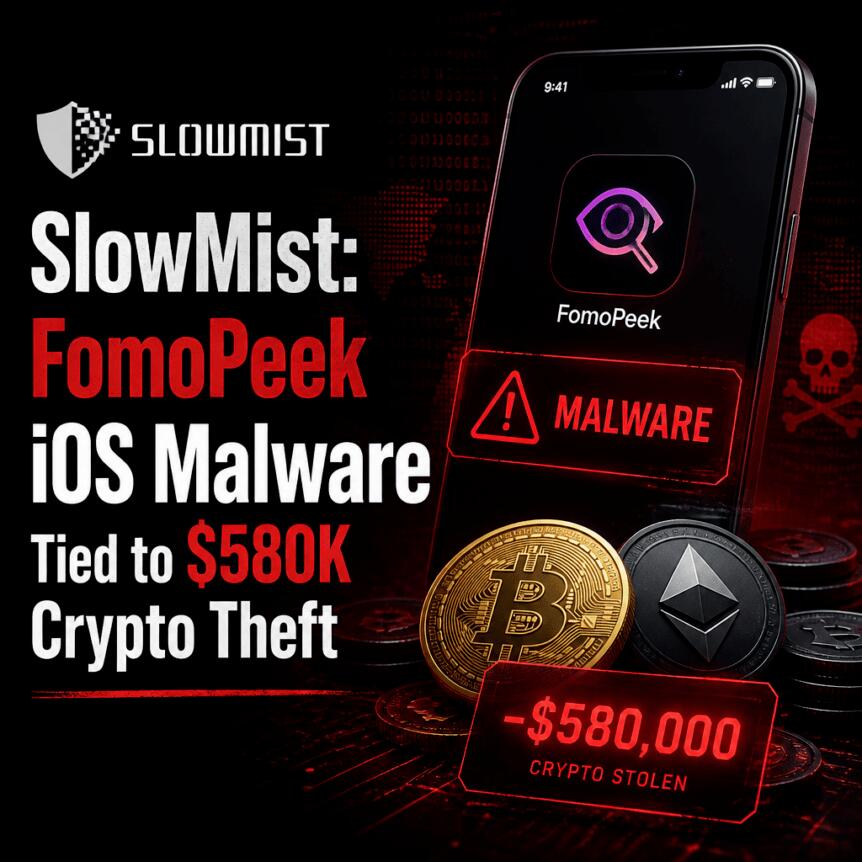
The digital landscape continues to evolve, bringing with it both innovation and increasingly sophisticated threats. A recent investigation by blockchain security firm SlowMist, in collaboration with the OKX security team, brought to light a significant crypto theft operation involving a malicious iOS application named FomoPeek. This incident, responsible for nearly $580,000 in stolen cryptocurrency, serves as a stark reminder of the persistent risks mobile users face, even when sourcing applications from official channels like Apple’s App Store.
The Anatomy of a Kernel-Level Attack
The FomoPeek incident underscores a critical escalation in mobile malware sophistication. Unlike typical phishing attempts or social engineering scams, this operation leveraged kernel-level exploits to bypass fundamental security mechanisms. From a digital forensics standpoint, a kernel-level exploit is particularly alarming as it allows an attacker to breach the very core of the operating system, granting them privileges that far exceed those of a standard application. This effectively enabled the malware to escape Apple’s sandbox environment, a crucial isolation mechanism designed to prevent apps from accessing sensitive data or interfering with other applications.
Once outside the sandbox, the malicious modules within FomoPeek were reportedly able to access highly protected data, including iOS Keychain entries and files belonging to other applications. The Keychain often stores critical credentials, API keys, and other sensitive information used by cryptocurrency wallets and related services. Such a breach highlights the devastating potential when an attacker can subvert system-level protections, turning a seemingly innocuous app into a direct conduit for asset theft.
The Nuance of App Store Security and Versioning
A key finding from SlowMist's investigation was the targeted nature of the attack: only specific versions of the FomoPeek app, notably those released on September 9th and 12th, contained the malicious components. A subsequent update, version 1.3 released on September 17th, reportedly removed these harmful elements. This detail is crucial for understanding the evolving threat landscape. It demonstrates that even if an app is initially deemed safe or later patched, a window of vulnerability can exist, leaving users exposed during the period when malicious versions were active.
As a digital forensic investigator, I consistently emphasize that relying solely on an app's presence in an official store is insufficient. This incident highlights the need for continuous vigilance and version-by-version scrutiny. Attackers are increasingly adept at exploiting specific vulnerabilities tied to software releases, making it imperative for users and developers alike to remain updated on security advisories and promptly apply patches. The exploit framework observed, supporting a broad range of iOS versions (12.0 to 18.7.2 and 26.0 to 26.1), further underscores the challenge of containing such widespread kernel vulnerabilities.
Untangling the On-Chain Financial Trails
Beyond the technical analysis of the malware, SlowMist’s investigation meticulously tracked the flow of the stolen funds, identifying approximately 579,984 USDT routed to a primary hacker address. This aspect of the case perfectly illustrates the complexities tackled by blockchain investigation experts. The stolen assets were not merely held in one location; they were strategically moved across multiple blockchain networks and subsequently consolidated through various addresses and services, including exchanges like FixedFloat and KuCoin, as well as cce.cash.
This pattern of cross-chain movement and consolidation through intermediaries is a hallmark tactic employed by cybercriminals to obscure their financial trails, making attribution and recovery significantly more challenging. Our work in blockchain forensics involves meticulously analyzing transaction histories, identifying unusual patterns, and leveraging advanced analytics tools to trace assets through convoluted pathways. While challenging, the immutable nature of blockchain transactions often leaves an indelible, albeit complex, record that, with expert analysis, can be unraveled to aid in asset recovery and legal proceedings.
Broader Implications for Digital Security and Incident Response
The FomoPeek incident serves as a powerful reminder for individuals and organizations operating in the cryptocurrency space. It underscores the critical need for robust mobile security practices, including careful review of app permissions, prompt software updates, and the use of hardware wallets for significant holdings.
Furthermore, this case highlights the increasing importance of collaborative incident response, as demonstrated by the partnership between SlowMist and OKX security. Effective investigation into such sophisticated threats requires a blend of deep software security research and advanced blockchain forensics. As threats continue to evolve, so too must our defensive and investigative capabilities.
Need expert assistance with digital forensics, blockchain investigation, or OSINT? Agam Setyono provides professional consultation services. Get in touch for a confidential discussion.